
Connect AI safely with company data.
Shield lets teams use AI safely with company data. Data, permissions and evidence can be checked before a request reaches Claude, ChatGPT, Codex or any approved model.
AI cannot bypass company control.
When teams connect AI to real data, the risk is not only what leaves the company. It is also what people inside the company can access through an AI answer.
If a user should not see payroll, contracts or sensitive customer records, AI must not become another path to that information.
Provider exposure
Sensitive data can reach external models before anyone has reviewed it.
Internal permission leakage
AI can answer from sources a user should not be able to access.
Missing evidence
Security and Compliance need records, not assumptions, when AI usage is reviewed.
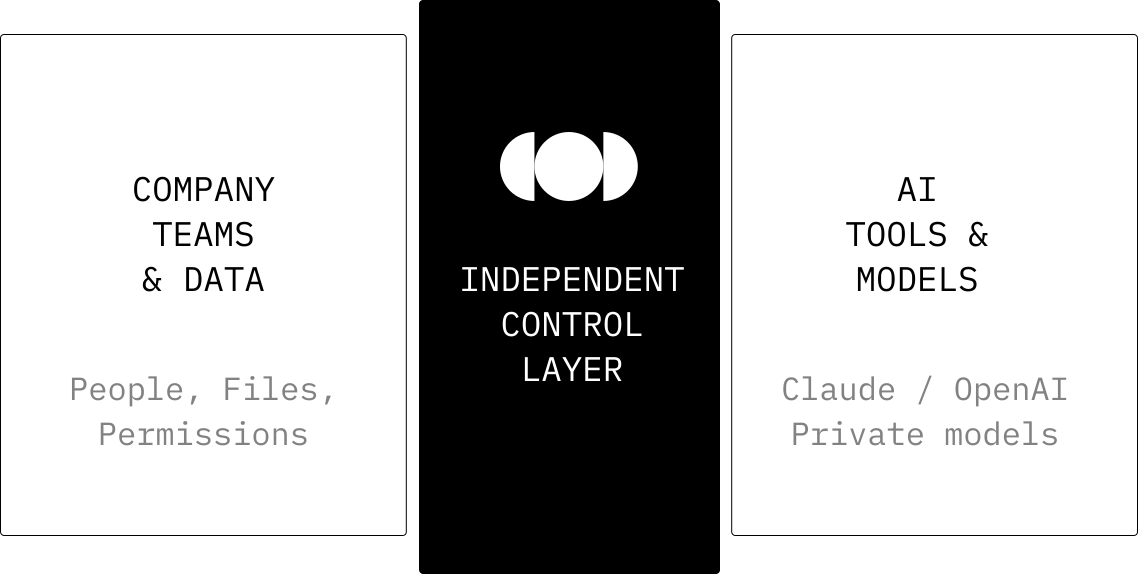
Shield checks every request before data reaches a model.
Every request passes through the same control layer. Shield checks identity, permissions, sensitive information, policies, spend limits and evidence before the request reaches an approved provider.
Approve AI with evidence, not trust.
Security teams should not have to rely on vendor promises or screenshots of settings. They need a record of what happened, which policy was applied and what data was allowed, removed or blocked.
Control data before it leaves
Sensitive information can be detected and stripped before an external model sees it.
Enforce internal permissions
AI answers follow the same access rules as the underlying company systems.
Keep an audit trail
Each request can produce evidence for internal review, governance and regulatory obligations.

AI security control board
Requests stopped by data, permission or policy rules.
Requests matched against existing access rights.
Models allowed to receive company requests.
Requests preserved for review and reporting.
Sensitive data
Define which data cannot leave the company, which data can be redacted and which requests must be stopped before reaching a provider.
- Block customer PII and financial identifiers by default.
- Allow redacted excerpts only when the user has source access.
Ask whatever you need to understand before moving forward.
Tell us what you are trying to approve, scale or review, or simply send the context you have right now.